

Learning with Fine-Grained Privacy
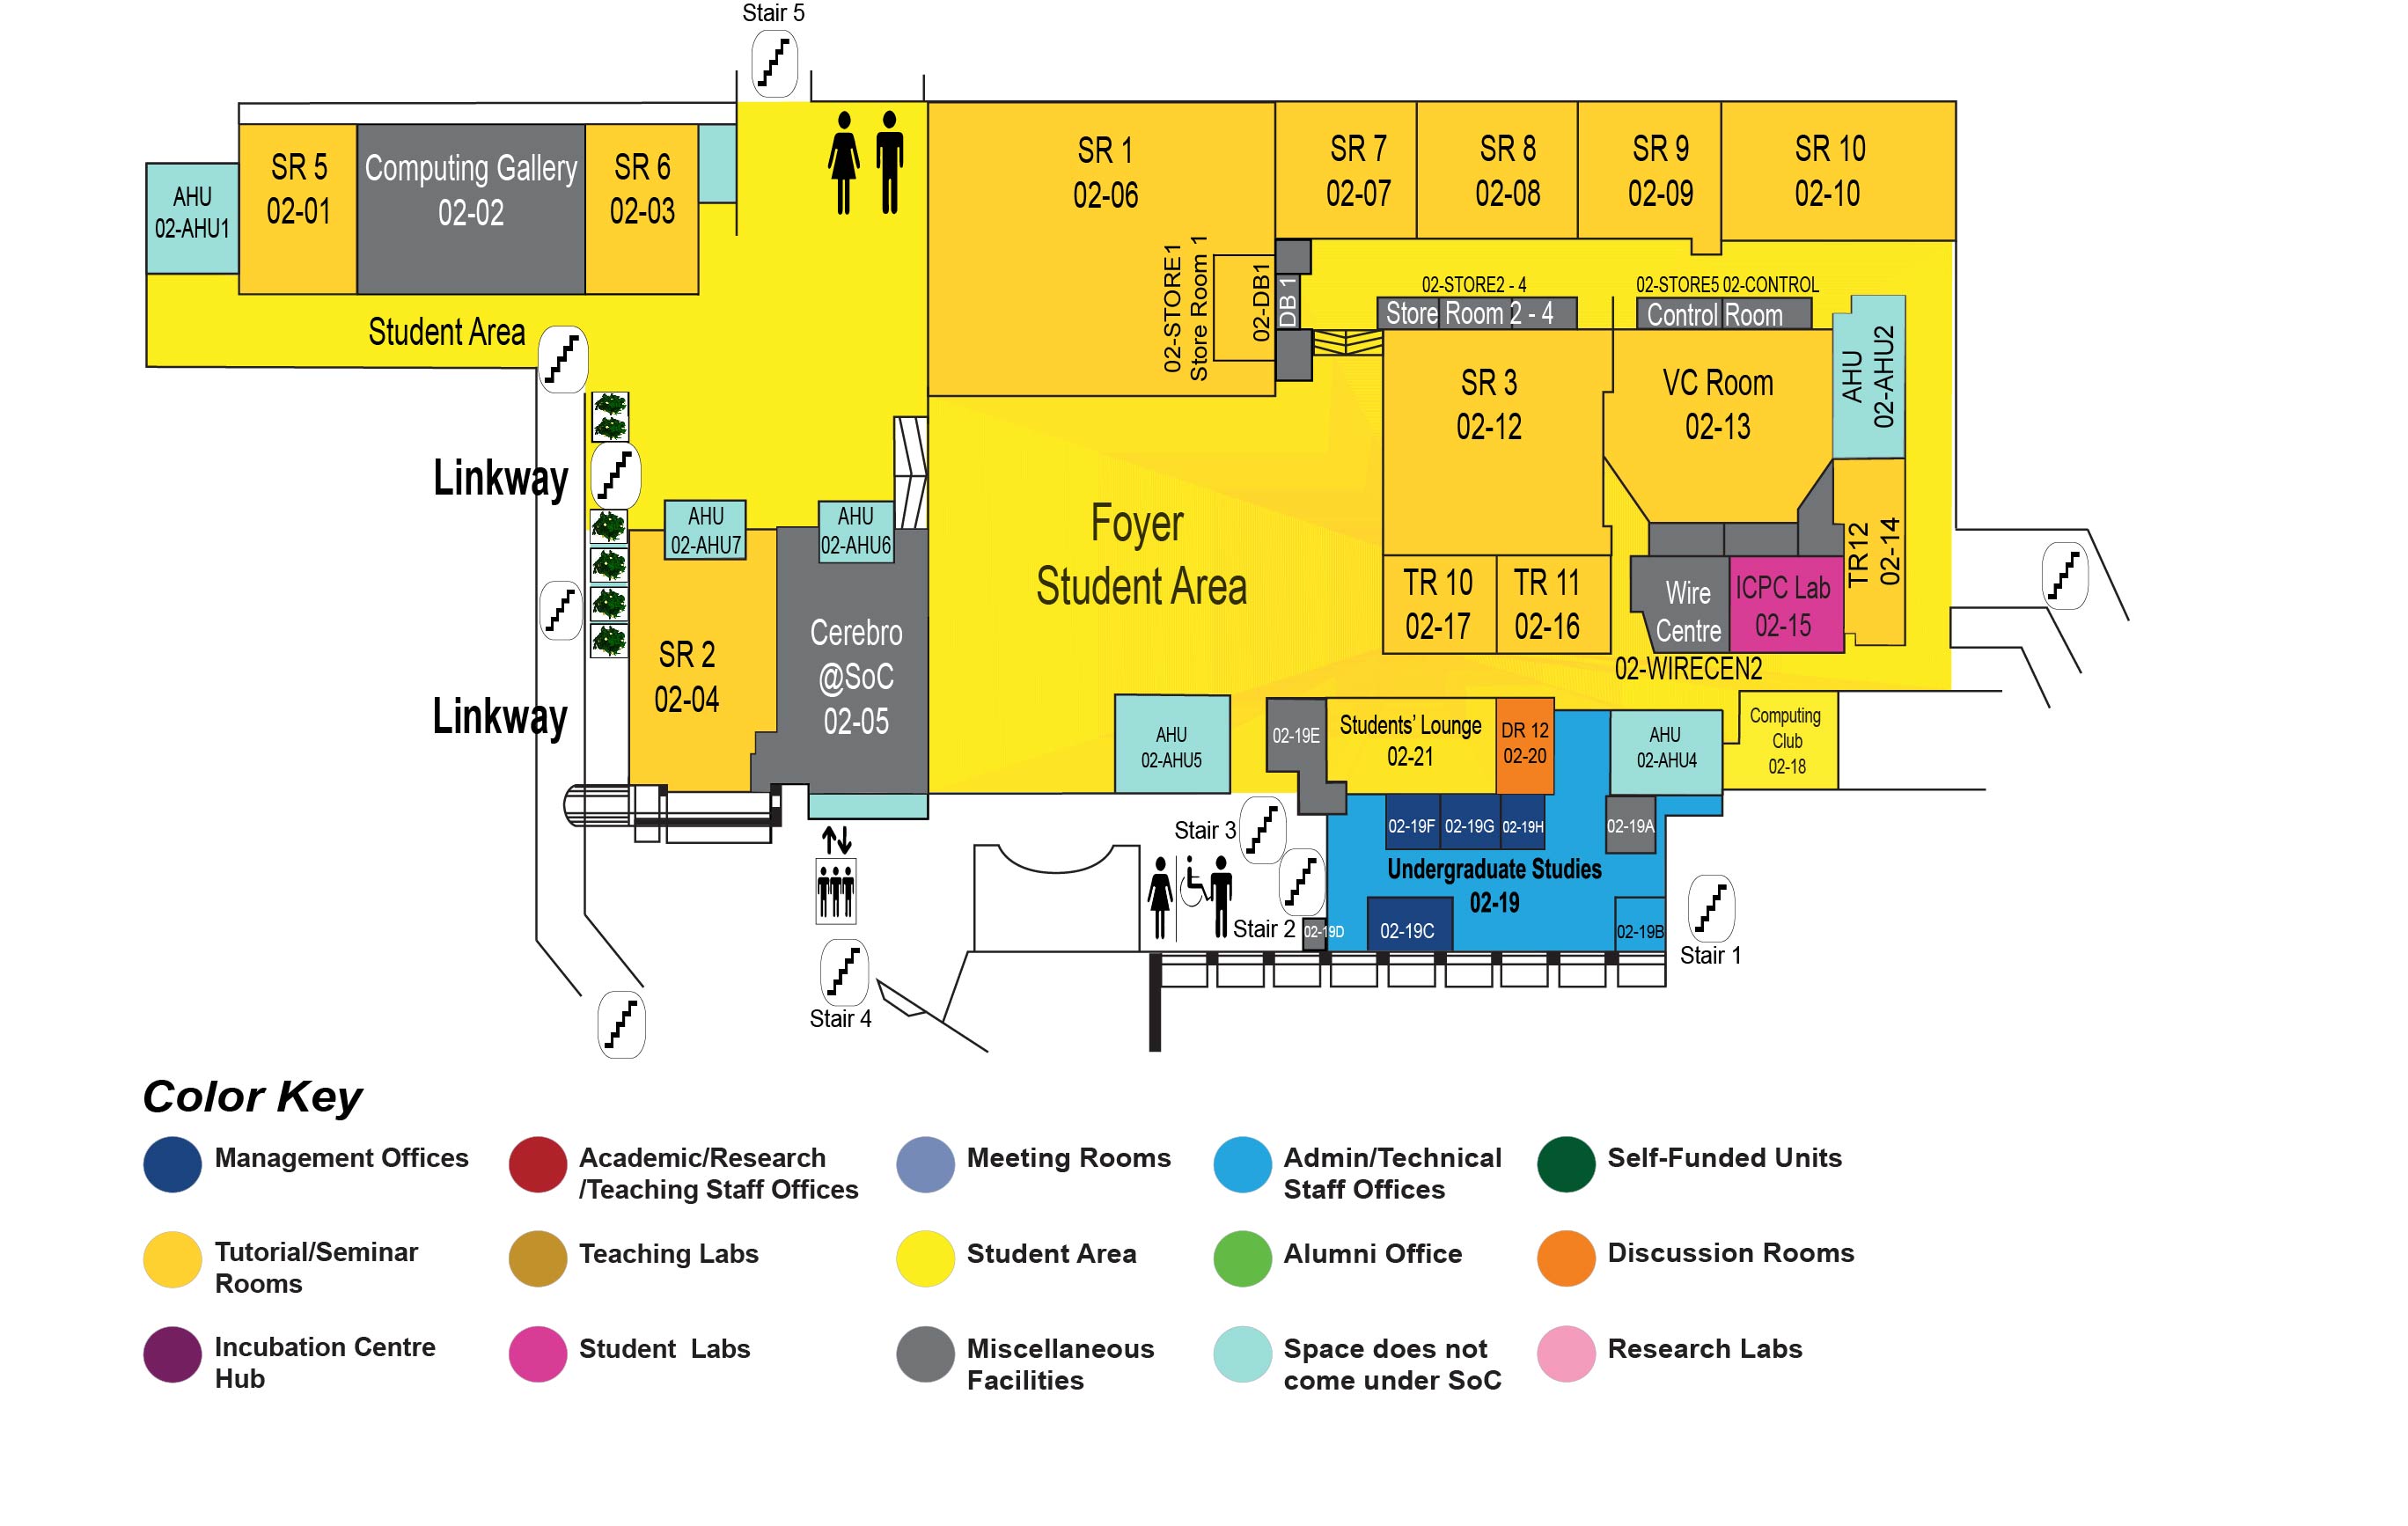
COM1 Level 2
SR10, COM1-02-10
Abstract:
Privacy is a central concern in modern AI, but standard differential privacy does not always match what is sensitive in practice. It can leave important information exposed or impose unnecessary utility loss. This thesis develops fine-grained privacy notions and learning algorithms for different types of sensitive information. We motivate the need for distribution-level protection, establish tight group privacy bounds that clarify the utility costs of broad distribution-level protection, and introduce label distributional privacy with an effective training method. We further study preference privacy for LLM alignment, formalizing protection for sensitive feedback and developing private preference optimization methods while preserving alignment quality.